Critical Security Vulnerability Discovered in PHP Programming Language
 ··1 min read
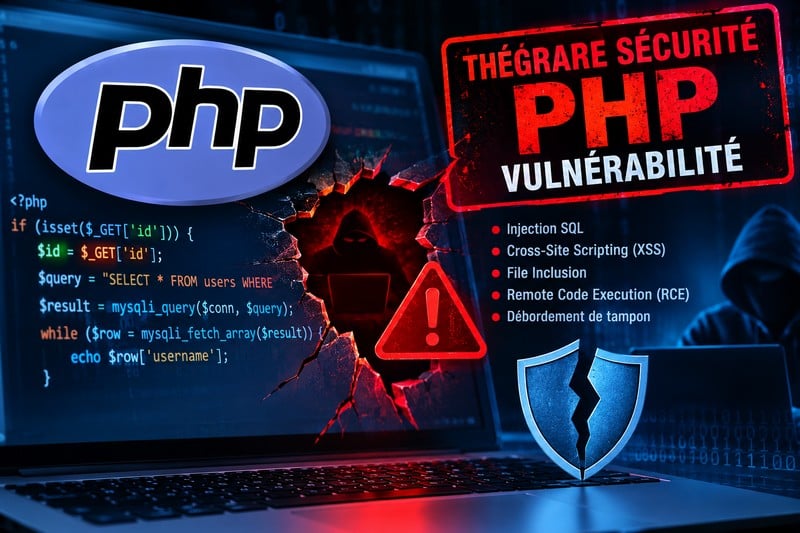
Security experts have identified a critical vulnerability in the PHP programming language, which is widely used on web servers worldwide. The vulnerability was detected on October 17, 2026, when it was first observed in a digital trap set by Amazon, known as a 'honeypot.' The honeypot is designed to lure attackers and monitor their activities.
Thomas Pol, a security expert at Check Point Software, has warned against a false sense of security, urging system administrators to take immediate and comprehensive actions beyond just installing security updates.
Pol recommends a thorough review of data logs, retroactively to October 17, 2026, to identify any potential breaches that may have occurred before the updates were installed. He also advises a complete renewal of login credentials and API keys.
Web Application Firewalls (WAFs), which act as a protective shield between web applications and the internet, are also crucial. WAFs analyze incoming data traffic and block malicious requests before they reach the system.
Pol emphasized the importance of conducting a full inventory of systems to identify where PHP components are used and the versions in operation. This is essential given the widespread use of PHP on web servers globally, which makes the vulnerability a significant risk.
If exploited, the vulnerability could serve as an entry point for attacks on internal networks.
CONTEXT: The vulnerability poses a significant risk to the security of web servers and internal networks, highlighting the need for comprehensive security measures beyond routine software updates.